Quick answer: Criminal forums and markets may advertise stolen data, but a listing is a lead to validate, not proof on its own. Effective monitoring connects credible exposure signals to a response plan.
Welcome Back
In the previous installment, we continued our unfiltered dive into the dark web by explaining the basics and diving into some general finds. Read Part 1 and Part 2 for context.
Before we start, we want to reiterate that playing around on the dark web can have serious repercussions. Given its daunting and enigmatic reputation, most people have never ventured out to see what really exists on the dark web. We'll give you a peek behind the curtain so that you don't have to put yourself at risk!
SEVN-X does not endorse or condone any material or activities mentioned in this article, nor does it seek to provide commentary or regard with bias any of the sites, users, or material depicted. Screenshots are included for educational purposes only.
Welcome to the Black Market
The last installment of our Dark Web Exposed series focused on entry level findings. It's time we dive into the darker side of the dark web and expose nefarious findings. We must give a disclaimer however as there are sinister applications on the dark web that we are not willing to touch on... use your imagination.
Things take a more sinister turn when we encounter a Black Market site. The historical screenshot below shows listings advertising identity documents and payment-card data. The seller’s claims and prices were not independently validated and should not be treated as current market facts.
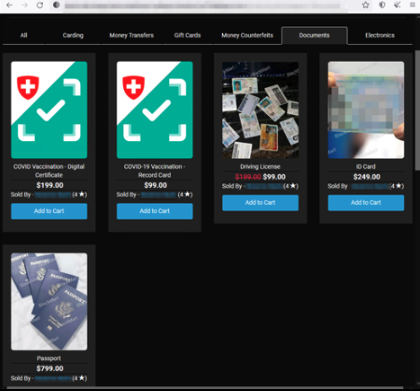 Black Market Sales Items
Breached Database Dumps?
Breached database dumps are sold in bulk and on a per-record basis on this site. When a threat actor breaches a network and exfiltrates data, that data frequently appears on dark web markets such as this, available for a price.
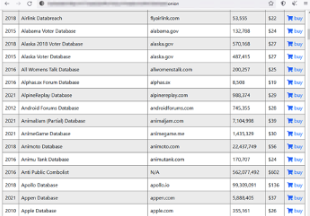 Database Dumps
In some cases, stolen data is published freely for all to see.

Once copied by an attacker, data may continue circulating beyond the organization’s control; removal of every copy cannot be guaranteed. Once it becomes available on the dark web, there is no telling who might get their hands on it and what they might do with it. Measures an organization can take to reduce this risk include efforts to prevent the data exfiltration from happening in the first place. Network monitoring solutions, privileged account management, and regular security assessments, such as penetration tests and vulnerability scans, are high-impact actions an organization can take to mitigate this risk.
At SEVN-X we're dedicated to helping create those safeguards so that you don't ever have to be a dark web statistic. If you have any questions about the services we provide or if you think that you aren't as secure as you should be, then don't hesitate ... the bad guys aren't!
You can submit your information requests on our website.
What to do with a credible exposure signal
- Record where and when the finding appeared without redistributing sensitive records.
- Validate whether the data belongs to your organization and whether it is new or historical.
- Bring confirmed findings to the incident-response owner and determine appropriate containment and account actions.
Frequently asked questions
Does a marketplace listing prove that a breach occurred?
No. Listings may be fabricated, recycled, or inaccurately attributed. Validate the claimed data, timing, and ownership before concluding that your organization was breached.
Can dark-web monitoring remove stolen data everywhere?
No. Monitoring can surface exposure signals, but cannot guarantee detection or removal of every copy. Use validated findings to drive containment, credential resets, and investigation.