DO WE HAVE AN IR QUOTE?? “The SEVN-X approach to penetration testing is unlike anything I have encountered in the past. Their innovative approach and deep skillsets not only reveal technology problems but also uncover people- and process-related problems. I consider our company more secure having partnered with SEVN-X.”
Avatar007

VP of IT Risk, Security, & Governance, Global Healthcare Company

INCIDENT RESPONSE / 24/7/365

Incident Response

Regain control and restore operations with rapid response, full recovery, and minimal disruption.

Download the service sheet ↓Immediate measures ↓
ACTIVE RESPONSE. LASTING READINESS.Global deployment / GIAC-certified expertise
FACING AN ACTIVE INCIDENT?

Start with a direct conversation.

Our team is on call 24/7/365 and ready to deploy worldwide within hours. Connect with a responder to establish the next steps.

+1 (484) 989-0911 ↗Immediate measures while you connect ↓
RESPONSE CAPABILITIES

From containment to recovery.

One coordinated effort across incident command, evidence, and technology.

Incident response team coordinating a response
01 / INCIDENT COMMAND

Stabilize the situation.

Rapid response and containment to take control, neutralize threats, and prevent further escalation. We coordinate the work required to restore critical systems with minimal disruption.

Response · Containment · Recovery
Digital forensics analyst examining evidence
02 / DIGITAL FORENSICS

Establish what happened.

Build a defensible narrative of the incident: how access occurred, what was affected, and what the evidence shows. Findings support recovery decisions and the questions raised by management, legal teams, and insurers.

Evidence · Impact · Root cause
Enterprise response technology deployment
03 / TECHNOLOGY DEPLOYMENT

Put the right controls in place.

Rapid delivery and deployment of enterprise-grade response software. Our response and remediation specialists guide triage, threat eradication, full remediation, recovery, and long-term monitoring.

Triage · Eradication · Monitoring
A CLEAR RESPONSE SEQUENCE

Clarity for the people making decisions.

01

Assess & mobilize.

Establish what is known, identify critical operations, and coordinate initial response priorities.

02

Contain & investigate.

Limit further exposure while preserving the evidence needed to understand the incident.

03

Eradicate & recover.

Remove the threat, remediate affected systems, and support a controlled return to operations.

04

Learn & strengthen.

Turn findings into clear remediation priorities, stronger controls, and improved response readiness.

IMMEDIATE MEASURES

Preserve your options.
Preserve the evidence.

Four critical actions while you connect with the response team.

01 / AFFECTED HOSTS

Disconnect from the network.

Avoid powering off affected hosts. Isolation limits further spread while preserving volatile memory and active forensic evidence.

02 / COMPROMISED SYSTEMS

Stop further use.

Continued use can enable additional exfiltration, malware deployment, or privilege escalation. Restrict use until responders validate that systems are safe to operate.

03 / THREAT ACTOR CONTACT

Engage trained negotiators.

Avoid contacting threat actors directly. Tactics vary by group, and the wrong opening move can lead to adverse reactions. Coordinate through experienced responders.

04 / CLEANUP & REMEDIATION

Speak to a breach coach first.

Premature cleanup can destroy the evidence chain needed for insurance, legal, and root cause analysis. Preserve evidence and coordinate collection before remediation.
BEFORE THE BREACH

Readiness is a leadership decision.

Strengthen the plans, workflows, and coordination you will rely on under pressure.

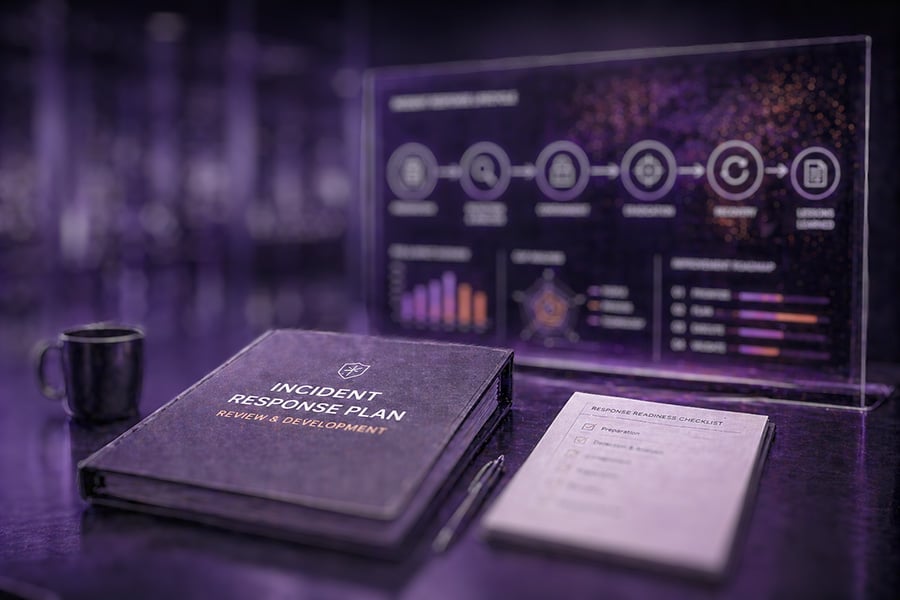
Incident response planning session

Plan review & development.

A focused, expert-driven review of your incident response strategy. Identify critical gaps, optimize workflows, and leave with prioritized recommendations and an actionable roadmap for stronger breach response capabilities.

Discuss your response plan ↗
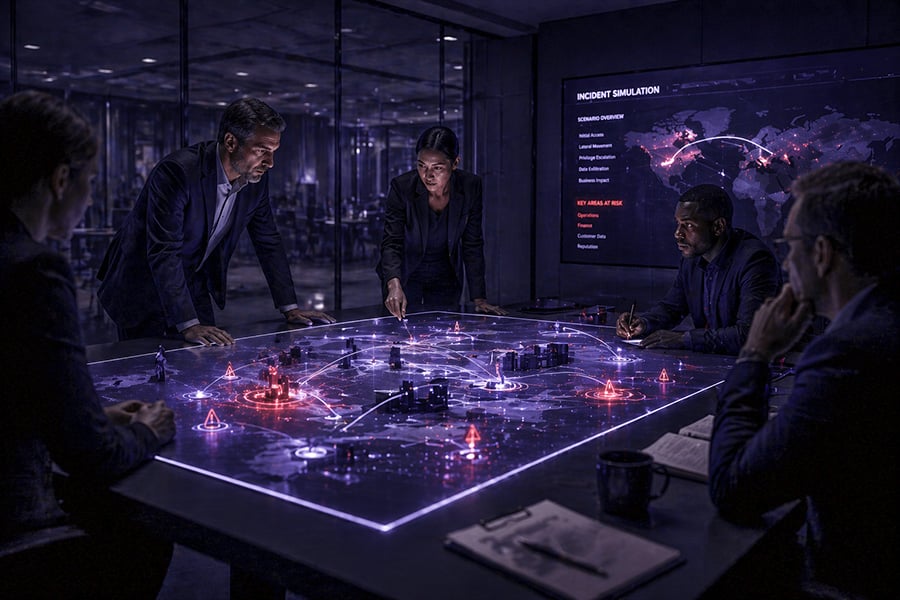
Executive and technical tabletop exercise

Executive & technical tabletops.

Tailored, realistic simulations that test incident response and crisis management across technical teams and executive leadership. Uncover gaps, assess readiness, and strengthen coordination before a real incident.

Explore tabletop exercises ↗
PUT YOUR NEXT STEP IN MOTION

Respond now. Prepare for what comes next.

Connect with an incident coach about an active event or your organization's readiness.

Contact an incident coach ↗